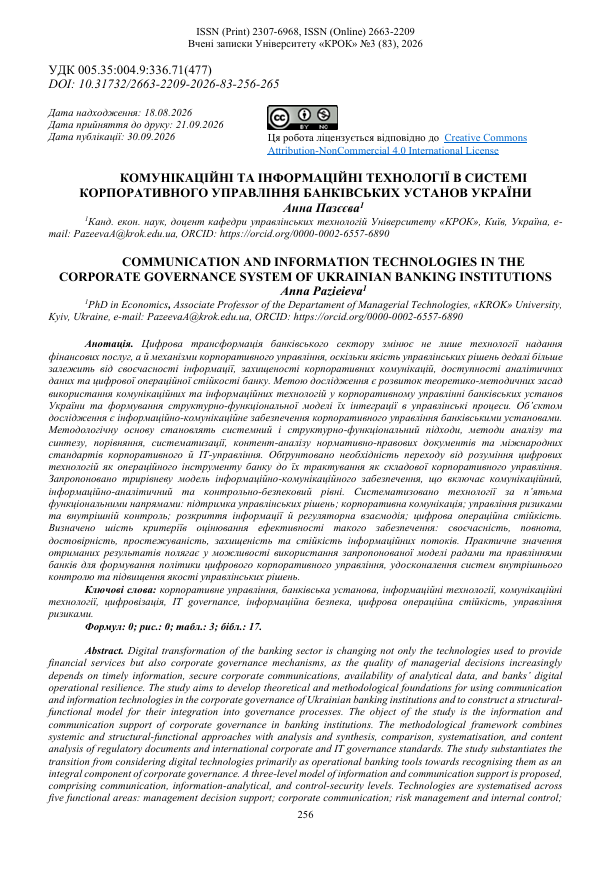
COMMUNICATION AND INFORMATION TECHNOLOGIES IN THE CORPORATE GOVERNANCE SYSTEM OF UKRAINIAN BANKING INSTITUTIONS
DOI:
https://doi.org/10.31732/2663-2209-2026-83-256-265Keywords:
corporate governance, banking institution, information technology, communication technology, digitalisation, IT governance, information security, digital operational resilience, risk managementAbstract
Digital transformation of the banking sector is changing not only the technologies used to provide financial services but also corporate governance mechanisms, as the quality of managerial decisions increasingly depends on timely information, secure corporate communications, availability of analytical data, and banks’ digital operational resilience. The study aims to develop theoretical and methodological foundations for using communication and information technologies in the corporate governance of Ukrainian banking institutions and to construct a structural-functional model for their integration into governance processes. The object of the study is the information and communication support of corporate governance in banking institutions. The methodological framework combines systemic and structural-functional approaches with analysis and synthesis, comparison, systematisation, and content analysis of regulatory documents and international corporate and IT governance standards. The study substantiates the transition from considering digital technologies primarily as operational banking tools towards recognising them as an integral component of corporate governance. A three-level model of information and communication support is proposed, comprising communication, information-analytical, and control-security levels. Technologies are systematised across five functional areas: management decision support; corporate communication; risk management and internal control; disclosure and regulatory interaction; and digital operational resilience. Six criteria for assessing the effectiveness of information and communication support are identified: timeliness, completeness, reliability, traceability, security, and resilience of information flows. The proposed approach integrates IT governance into the overall corporate governance architecture and clarifies the responsibilities of the supervisory board, management board, risk management, compliance, internal audit, and IT functions. The practical significance of the findings lies in the possibility of applying the proposed model by supervisory and management boards of Ukrainian banks when developing digital governance policies, improving internal control systems, managing ICT-related risks, and increasing the quality and transparency of corporate decision-making.
Downloads
References
Basel Committee on Banking Supervision. (2015). Corporate governance principles for banks. Bank for International Settlements. https://www.bis.org/bcbs/publ/d328.htm
Basel Committee on Banking Supervision. (2021). Principles for operational resilience. Bank for International Settlements. https://www.bis.org/bcbs/publ/d516.htm
Caluwe, L., & De Haes, S. (2019). Board level IT governance: A scoping review to set the research agenda. Information Systems Management, 36(3), 262–283. https://doi.org/10.1080/10580530.2019.1620505
Caluwe, L., Wilkin, C. L., De Haes, S., & Huygh, T. (2024). Board roles required for IT governance to become an integral component of corporate governance. International Journal of Accounting Information Systems, 54, 100694. https://doi.org/10.1016/j.accinf.2024.100694
De Haes, S., & Van Grembergen, W. (2009). An exploratory study into IT governance implementations and its impact on business/IT alignment. Information Systems Management, 26(2), 123–137. https://doi.org/10.1080/10580530902794786
European Banking Authority. (2021). Guidelines on internal governance under Directive 2013/36/EU. https://www.eba.europa.eu/activities/single-rulebook/regulatory-activities/internal-governance/guidelines-internal-governance
European Parliament & Council of the European Union. (2022). Regulation (EU) 2022/2554 of 14 December 2022 on digital operational resilience for the financial sector. Official Journal of the European Union, L 333, 1–79. https://eur-lex.europa.eu/eli/reg/2022/2554/oj
OECD. (2023). G20/OECD principles of corporate governance 2023. OECD Publishing. https://doi.org/10.1787/ed750b30-en
Weill, P., & Ross, J. W. (2004). IT governance: How top performers manage IT decision rights for superior results. Harvard Business School Press.
Національний банк України. (2018). Про затвердження Положення про організацію системи управління ризиками в банках України та банківських групах: Постанова Правління Національного банку України від 11.06.2018 № 64. https://zakon.rada.gov.ua/laws/show/v0064500-18
Національний банк України. (2019). Про затвердження Положення про організацію системи внутрішнього контролю в банках України та банківських групах: Постанова Правління Національного банку України від 02.07.2019 № 88. https://zakon.rada.gov.ua/laws/show/v0088500-19
Національний банк України. (2021). Про затвердження Положення про захист інформації та кіберзахист учасниками платіжного ринку: Постанова Правління Національного банку України від 19.05.2021 № 43. https://zakon.rada.gov.ua/laws/show/v0043500-21
Національний банк України. (2025a). Про затвердження Змін до деяких нормативно-правових актів Національного банку України з питань інформаційної безпеки та кіберзахисту: Постанова Правління Національного банку України від 25.02.2025 № 24. https://bank.gov.ua/admin_uploads/law/25022025_24.pdf
Національний банк України. (2025b). Про затвердження Положення про відкритий банкінг в Україні: Постанова Правління Національного банку України від 25.07.2025 № 80. https://bank.gov.ua/ua/payments/open-banking
Національний банк України. (2025c). Про затвердження Положення про порядок застосування технології хмарних обчислень: Постанова Правління Національного банку України від 25.08.2025 № 99. https://zakon.rada.gov.ua/laws/show/v0099500-25
Національний банк України. (2026). Про затвердження Положення про встановлення підвищених значень пруденційних нормативів для банків України: Постанова Правління Національного банку України від 28.05.2026 № 57. https://zakon.rada.gov.ua/laws/show/v0057500-26
Пуш, А., Мігус, І., & Наконечна, Н. (2024). Основні моделі корпоративного управління в банківських установах. Вчені записки Університету «КРОК», 2(74), 204–216. https://doi.org/10.31732/2663-2209-2024-74-204-216
Downloads
Published
How to Cite
Issue
Section
License

This work is licensed under a Creative Commons Attribution-NonCommercial 4.0 International License.